

- Article
- Comments (0)
India: data protection
WILL WE ENTER THE MATRIX EVER?
India ardently needs to build a measure to secure data
Tags : Mumbai | Uzbekistan |
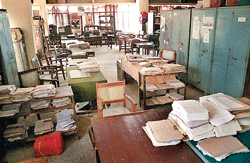 A major fire at Mumbai Mantralaya, on June 21, 2012 put paid to much data collated to bring the culprits of Adarsh Housing Scam to books. Out of 500 odd computers that were placed in the gutted level, only 50 could be recovered. A similar fire gutted a small part of the North Block in Delhi on June 24, 2012... One saw various government departments springing to action to ensure that in the future, such incidents are handled well. Sadly, the same cannot be said of our government's commitment to prevent cyber hacking of critical government servers and computers.
The cyber hacking of our national data has increased fourfold in last four years, exposing the fact that our data security can be breached too easily. Apart from this, our ministries’ computer systems and our precious data are subject to virus attacks at the drop of the hat as was the case with the Home Ministry in 2010. The account of India’s Ambassador to Uzbekistan was infected with virus and an infected mail was sent from the account to the Home Ministry.
The Indian laws regarding data safety (IT Act 2000 and Personal Data Protection Bill 2006) are too feeble and largely perforated by loopholes. The "Draft Discussion Paper on Privacy Bill” only advocates the right to protect the personal information but there is no mechanism to implement it effectively. It only underscores the fact that there is neither a realistic long term plan nor is there any concern for data security.
India should take a lesson or two from the strong data privacy protection laws of the US, which has segmented their data allowing assignment of varying degrees of protection according to its importance. Several data protection legislations i.e., the Privacy Act, Electronic Communications Privacy Act, Children’s Online Privacy Protection Act, and Consumer Privacy Protection Act; provide necessary buffer against illegal access and hacking of data by safeguarding it prudently. The pillar of data protection in UK is the Data Protection Act that was enacted in 1984 and later modified in 1998. All personal details like addresses, phone numbers, e-mail addresses are included in the act.
One of the major drawbacks in Indian legislations for data security is the fact that it’s not classified into segment groups. Therefore, assigning weightages according to varying degree of importance becomes unrealistic. Further, our IT Act profoundly deals with extraction of data and is ineffective for its protection. Another important reason for the poor state of data security in our country is the federal squeeze of funds. India is spending peanuts compared to total expenditure of $11billion that the US government spends on preserving its data. With Wikileaks and cyber attacks (Stuxnet virus) taking the toll on the world's data security systems, the US has not only increased the budget, but also passed an executive order in October, 2011 directing “federal agencies to implement new measures to limit access to classified networks and data”. Similar executive orders were passed in 2009 to make data classification more standardised and secure. The Indian policy makers need to realise the urgency of the situation, one which can eventually bring our nation to a standstill – both economically and politically.


 Issue Dated: Feb 5, 2017